For years, enterprise security teams have operated with an implicit assumption: once a vulnerability is disclosed or an attacker gains an initial foothold, defenders have a reasonable window to detect, investigate, and respond.
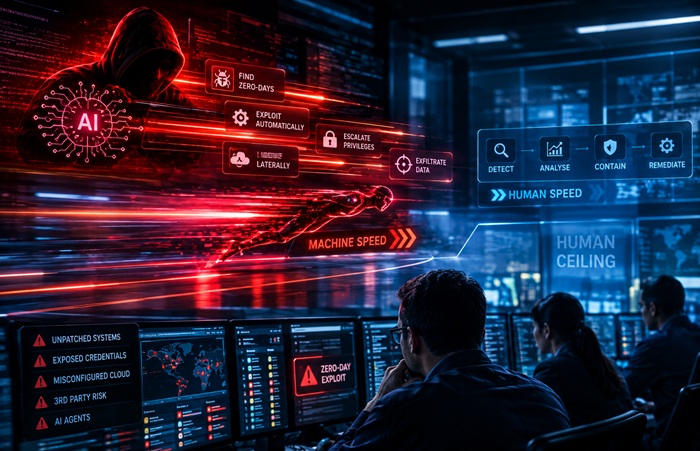
Artificial intelligence is now dismantling that assumption. The immediate concern is not that cybercriminals have handed entire campaigns over to fully autonomous systems. Instead, AI allows conventional attackers to move faster, automate key stages of the attack chain, and execute complex techniques at machine speed.
For Chief Information Security Officers (CISOs), the problem has become a race between machine-accelerated exploitation and human-paced enterprise decision-making.
The Remediation “Human Ceiling”
The clearest evidence of this acceleration is emerging around vulnerability management. Attackers no longer wait for official Common Vulnerabilities and Exposures (CVE) designations before planning and executing breaches.
“Frontier AI models are finding novel vulnerabilities at machine speed. These AI models can now discover and help weaponise vulnerabilities far faster than organisations can manually triage them,” says Debashish Jyotiprakash, Vice-President, Asia and ANZ at Qualys.
“Attackers do not wait for CVEs before planning and executing a breach. Hence, defenders should not depend on them either. This is a gap we have been closing for years, which is why Qualys today ships more than 17,000 detection signatures for vulnerabilities that have no CVE assigned.”
The scale of this operational gap is detailed in the Qualys Threat Research Unit (TRU) report, The Broken Physics of Remediation, which analyzed over one billion Known Exploited Vulnerabilities (KEV) remediation records across more than 10,000 organizations from 2022 to 2025.
The findings reveal a severe structural limitation: while total closed vulnerabilities rose sharply from 73 million in 2022 to 473 million in 2025, security outcomes actually worsened. The percentage of critical vulnerabilities remaining open at Day 7 increased from 56% to 63%. This widening gap reflects a “human ceiling,” where the speed and volume of incoming risks outpace human remediation capacity.
Qualys TRU Remediation Metrics (2022–2025 Analysis)
- Analysis Scope: Over 1 billion KEV remediation records analyzed across 10,000+ organizations.
- Total Closed Vulnerabilities (2022): 73 million.
- Total Closed Vulnerabilities (2025): 473 million.
- Open Critical Vulnerabilities at Day 7: Increased from 56% to 63%.
- Time-to-Exploit: Dropped to -1 day (exploited before patches are available).
- Unpatched Assets at Disclosure: 85%.
- Unpatched Assets at Day 7 (Week 1): 63%.
- Unpatched Assets at Day 21: 33%.
- Unpatched Assets at Day 90: ~12%.
The report shows that Time-to-Exploit has dropped to -1 day, meaning vulnerabilities are frequently exploited before vendor patches are even available. At the time of disclosure, 85% of assets remain unpatched. One week later, 63% remain exposed; after three weeks, 33% are still vulnerable; and nearly 12% remain unpatched after 90 days.
“When Time-to-Exploit drops into negative territory, keeping any security gap open gives attackers the runway to automate exploitation straight to breach,” Jyotiprakash emphasizes.
“Once vulnerabilities are validated and prioritised, the primary challenge for CISOs shifts to managing remediation throughput. And since manual remediation is no longer viable, it must transition into an automated workflow built on operational resilience.”
Asymmetric Speed and the Breakout Reality
This operational bottleneck creates an uncomfortable asymmetry. Defenders must navigate multi-step internal approvals, change-management boards, downtime scheduling, and manual asset tagging. Attackers encounter none of these speed bumps.
The shift in threat patterns is underscored by Verizon’s 2026 Data Breach Investigations Report, which revealed that vulnerability exploitation accounted for 31% of breaches, overtaking credential abuse as the primary initial-access vector for the first time in the report’s 19-year history.
Yet, enterprise resolution times are slowing down: Verizon found the median time to fully resolve a vulnerability increased from 32 days to 43 days, while only 26% of vulnerabilities in CISA’s Known Exploited Vulnerabilities catalog were remediated in 2025, down from 38% in 2024.
Telemetry from CrowdStrike highlights the same speed dynamic on the endpoint. The company reported that the average eCrime breakout time—the time it takes for an attacker to move laterally from an initial access point to other systems—fell to 29 minutes, with the fastest observed breakout taking just 27 seconds. Furthermore, 82% of detections were malware-free, relying instead on hands-on-keyboard techniques or stolen credentials.
Sujit Christy, Chair of the ISC2 Chapter Regional Management Committee for APAC, categorizes the threat landscape into three operational tiers: automated attacks requiring no AI, such as traditional worms or bots; AI-assisted attacks where humans use AI for tactical speed; and autonomous exploitation where AI agents independently execute attack steps.
“Three different answers to who’s making the decisions,” Christy observes. “The real gap isn’t readiness for autonomous attackers. It’s basic patching, vendor vetting, and knowing what your own AI agents can actually do before one surprises you.”
Real-World Intrusion Timelines
AI-driven campaign acceleration is already occurring in active environments. Cisco Talos recently documented threat group UAT-10147 targeting Windows and Linux web servers globally using AI-driven tooling across reconnaissance, payload generation, validation, and persistence. Talos observed AI-generated operational playbooks, automated exploit scripts, and real-time troubleshooting logic deployed during active intrusions.
Google Threat Intelligence Group reported a similar shift in its late-2026 threat assessment, noting that threat actors are transitioning from simple prompt engineering to agentic workflows. In one Q2 operation, attackers compromised a cloud resource and used agent-enabled automation to plan, build, and execute a mass credential-harvesting campaign in under six hours.
Local Reality for Regional CISOs
For Indian organizations, these global speed pressures arrive alongside high volumes of conventional security incidents. CERT-In tracked 2,944,248 cybersecurity incidents in 2025, up from 2,041,360 in 2024 and 1,592,917 in 2023. CERT-In’s activities included issuing 1,530 alerts, 390 vulnerability notes, and 65 advisories, as well as conducting 122 security drills across critical sector organizations.
Ransomware activity has escalated in tandem. Cyble’s Q1 2026 Asia-Pacific threat assessment recorded 45 ransomware incidents in India, representing a 165% year-on-year increase across key industries including IT, manufacturing, healthcare, BFSI, and automotive.
The practical takeaway for CISOs is clear: legacy patch processes and manual triage workflows cannot defend against AI-assisted attack vectors.
The challenge is no longer just identifying flaws or deploying better detection tools. It is establishing automated, resilient remediation workflows capable of making security decisions and executing responses faster than an attacker can move.