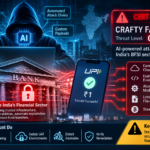
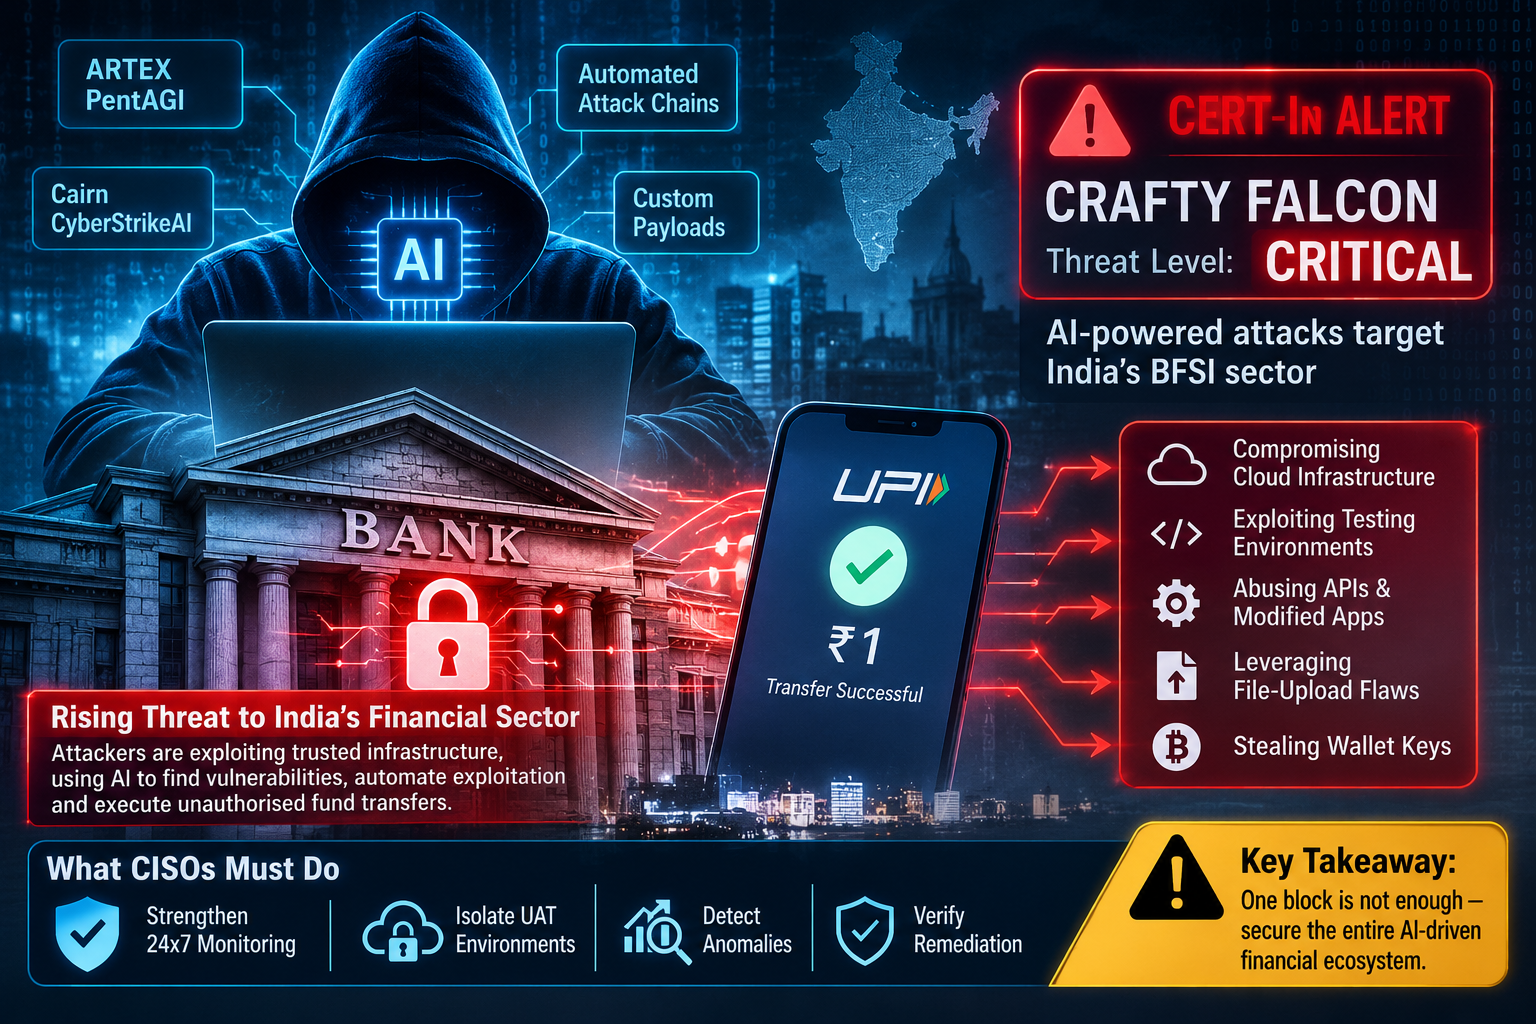
India’s banking and financial services sector is facing an escalating cyberattack campaign in which threat actors use artificial intelligence to find vulnerabilities, automate exploitation and execute unauthorised financial transactions.
The Indian Computer Emergency Response Team (CERT-In) has designated the actor behind the campaign CRAFTY FALCON and rated the threat critical. Its alert updates an October 9 warning about attackers abusing payment and disbursement APIs to trigger unauthorised fund transfers. Incidents reported by NBFCs, digital lending platforms, fintechs, payment aggregators, payment service providers and cryptocurrency exchanges point to a significant escalation.
How the attacks work
Attackers are using offensive security tools including ARTEX, PentAGI, Cairn and CyberStrikeAI. These can run attack chains autonomously, generate customised scripts and alter their payloads based on how target systems respond.
Abuse of trusted infrastructure. CERT-In says the campaign is especially worrying because attackers exploit institutions’ own infrastructure and trusted application interfaces. The techniques it identified include:
- Compromising cloud infrastructure
- Exploiting internet-facing testing environments, then moving into production through shared credentials, tokens and network connections
- Reverse-engineering application code to build custom exploits
- Making unauthorised API calls through modified application packages, which defeats controls that assume requests come only from legitimate client apps
- Exploiting newly disclosed file-upload and deserialization flaws in PHP and Node.js applications
- Stealing wallet keys from cryptocurrency platforms and siphoning funds
Attackers run small test transactions, sometimes as low as ₹1, to confirm an unauthorised fund flow works before attempting larger transfers. Payment aggregator merchant settlement APIs have also been abused to move money.
CERT-In says operations were deliberately scheduled around weekends, holidays and periods of reduced monitoring to delay detection and response.
Repeat attacks expose remediation gaps
Perhaps the most worrying finding is that some organisations that were previously alerted and advised to fix their vulnerabilities have been targeted again.
Cybersecurity practitioners assessing the advisory pointed to successful repeat attacks on organisations that had already remediated, and attributed the continued exposure to incomplete remediation and weak cloud, application and API controls.
They urged security teams to watch for three indicators:
- ₹1 test transactions
- Modified mobile applications
- Attacks timed around holidays or reduced monitoring
Their core warning for every CISO managing incident recovery: blocking an attacker once does not mean the threat has been eliminated.
What CISOs should do
Traditional vulnerability management, periodic penetration testing and perimeter-focused controls may not be enough against attackers that operate autonomously and continuously.
Experts recommend strengthening 24×7 security operations centre monitoring, isolating user acceptance testing (UAT) environments from production systems and investigating suspicious cloud activity. Finance and application teams should also monitor low-value test transfers, enforce transaction limits and verify beneficiaries.
CERT-In calls for heightened monitoring, stronger cloud security, isolation of testing environments, identity-based API controls and transaction anomaly detection. The advisory also recommends automated containment, zero-trust architecture and forensic verification following incidents.
The Way Forward
Security must now cover the entire ecosystem of APIs, cloud services, third-party integrations and payment workflows that make financial transactions possible, not just banking applications. As AI shrinks the time and effort needed to find and exploit weaknesses, the window for defenders is closing. Organisations must also confirm through forensic verification that an attacker is fully removed before they declare an incident resolved.
Nair is a seasoned cybersecurity journalist with over a decade of experience covering cybersecurity and OT developments in the US and the Asia-Pacific region. As an editor, he has interviewed key decision-makers, including CISOs, CIOs, regulators and law enforcement leaders. Before joining ObserveNow, Nair held editorial roles at Information Security Media Group, News Corp owned TechCircle, IDG, The Times Group and The New Indian Express. He is currently based in Bilaspur, India.