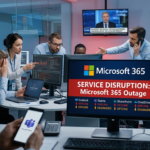
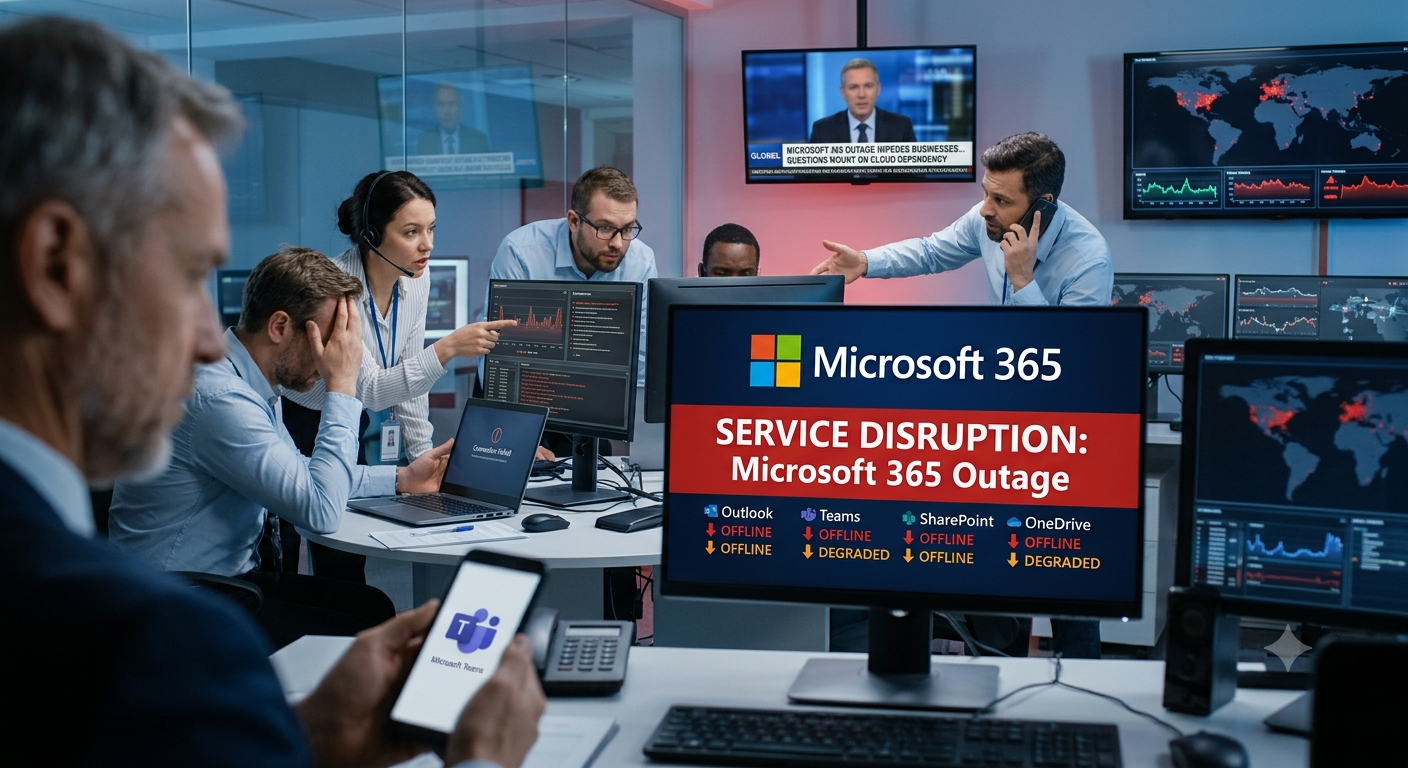
A widespread global outage across Microsoft’s cloud ecosystem has left millions of professionals, enterprises, and government agencies scrambling since Thursday evening, disrupting core workplace tools including Exchange Online (Outlook), Microsoft Teams, OneDrive, SharePoint, and Microsoft 365 Copilot.
Reports of service failures spiked globally into Friday morning, with government institutions in the UK, Australia, Japan, and the US among those reporting communication bottlenecks, and financial traders in Singapore and Taiwan falling back on phone calls and WhatsApp to confirm deals.
Third-party AI integrations relying on Microsoft’s connectors, including OpenAI and Anthropic, also experienced ripple-effect interruptions. In its latest service update on Friday, Microsoft said that it is scaling up virtual machines and deploying software patches, reporting early “positive results for server stability” as affected systems gradually come back online. Both Microsoft Copilot executive Charles Lamanna and Microsoft’s official service status page reiterated that the company has found no indication of a cyberattack or malicious activity.
Speaking to CISONow on condition of anonymity, the Chief Information Security Officer (CISO) of an Indian public sector undertaking (PSU) confirmed that the outage had disrupted internal operations. The executive noted that while Microsoft has attributed the incident to server capacity and stability issues, widespread speculation has circulated across security circles regarding a potential cyberattack, including unverified theories pointing to possible Chinese state-sponsored threat actors.
For Indian enterprises and security leaders, the prolonged downtime has reignited an uncomfortable debate around cloud concentration risk and business continuity.
Reacting to the disruption, Adv. (Dr.) Prashant Mali, International Cyber Law, Data Protection, and AI Law Expert pointed out the fragility of single-vendor cloud reliance:
“Microsoft Outlook has decided to take an unscheduled vacation, without informing HR, seeking leave approval, or even putting an Out of Office message. Millions of professionals are discovering an uncomfortable truth today: their productivity, apparently, was sitting inside someone else’s server. Emails are not arriving, meetings are hanging in limbo, deadlines are sweating, and executives are repeatedly clicking Refresh as if it were a prayer button.
The irony is delicious, Microsoft sells cloud-powered productivity, but when the cloud develops a fever, the entire corporate world catches a cold. Perhaps this is the perfect reminder that digital transformation without digital resilience is merely dependency dressed up as innovation. I would suggest keeping a standalone version of Microsoft Office as backup, as Microsoft 365 today has become Microsoft 364.”
Sujit Christy, Founder and Director of Layers-7 Seguro Consultoria and Board Member at ISACA Sri Lanka Chapter, said that while the outage had a global footprint, systems are gradually recovering as Microsoft releases targeted updates to restore affected infrastructure.
He observed that although the incident had wide visibility, its core technical impact was concentrated in a specific service vertical while other cloud operations continued, meaning organizations heavily dependent on cloud email and adjacent collaboration workflows bore the brunt of the disruption.
For Christy, the incident serves as a wake-up call for enterprise risk governance:
“We are going through a reset. Organisations need to ask themselves where their dependencies lie and where they need to establish resilience.”
The CISO Takeaway
While Microsoft confirmed the incident stems from server capacity and stability issues rather than a breach, security and risk leaders cannot treat availability outages separately from cyber resilience:
Audit single points of failure: When email, collaboration, identity routing, and security consoles share the same cloud dependency path, an upstream failure paralyzes both daily operations and incident coordination.
Maintain out-of-band backups: Ensure executive teams and SOCs have independent communication channels and offline/standalone productivity contingencies ready before the next cloud disruption hits.
Nair is a seasoned cybersecurity journalist with over a decade of experience covering cybersecurity and OT developments in the US and the Asia-Pacific region. As an editor, he has interviewed key decision-makers, including CISOs, CIOs, regulators and law enforcement leaders. Before joining ObserveNow, Nair held editorial roles at Information Security Media Group, News Corp owned TechCircle, IDG, The Times Group and The New Indian Express. He is currently based in Bilaspur, India.